
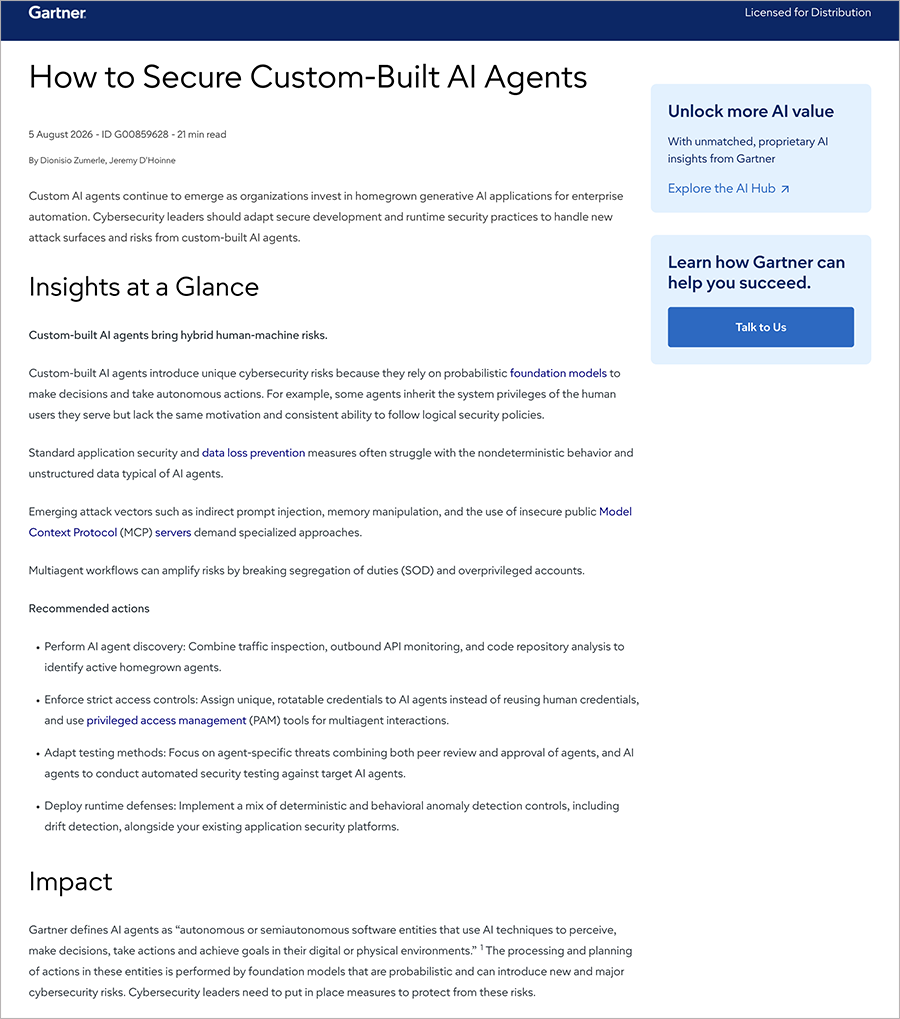
Custom-built AI agents introduce new cybersecurity risks because they rely on probabilistic AI models to make decisions and take actions autonomously. This Gartner report discusses how security leaders can adapt existing security practices to discover, test, control, and protect AI agents throughout their lifecycle.
In this, you’ll find:
- Why standard application security and DLP measures fall short against nondeterministic AI agent behavior
- How to enforce access control across single and multi-agent workflows without breaking segregation of duties
- Insights for adapting your secure development life cycle to agentic threats, including indirect prompt injection and memory manipulation
- Runtime defense strategies that combine deterministic controls with behavioral anomaly detection to catch AI-specific attacks
Key details:
- Access control issues will be the cause of most agentic security failures
- Most published MCP servers lack content sanitization, making public MCP servers a significant and underestimated attack vector
- Secure your AI agents before they become an enterprise risk
Get the Gartner insights on building a security approach for custom-built AI agents—from discovery and access control to security testing and runtime defense.
Download the Gartner report How to Secure Custom-Built AI Agents.
Download the Gartner report How to Secure Custom-Built AI Agents.
Gartner, Inc. How to Secure Custom-Built AI Agents. Dionisio Zumerle, Jeremy D'Hoinne. 5 August 2026.
GARTNER is a trademark of Gartner, Inc. and/or its affiliates.